Implicit Collaboration Capabilities Beyond the Industrial Control Computer Industry Certification System
Implicit Collaboration Capabilities Beyond the Industrial Control Computer Industry Certification System
To the untrained eye, the certification system of the industrial control PC industry resembles a thick technical dictionary. 3C, CE, FCC, RoHS, IP65, EMC, UL, ISO 9001… these letter combinations are densely packed in product specifications and tender documents, forming a self-evident industry language. However, in the eyes of experts, these certifications are not monolithic commodities. They have strict hierarchical distinctions, clear jurisdictional boundaries, and real value that is activated only in specific scenarios. More importantly, once all suppliers can produce these certificates, what truly distinguishes the quality of cooperation lies in what the certificates themselves cannot cover.
Let's start with the most basic entry requirements. 3C certification, or China Compulsory Certification, is a legal requirement for industrial control PCs sold in the domestic market. Without it, a product doesn't even qualify to enter the market. It proves that the product meets national standards in basic indicators such as safety and electromagnetic compatibility, but that's all—3C is an entry ticket, not a certificate. The corresponding international version is CE certification, a passport to the EU market, which also represents a basic declaration that the product meets EU safety, health, and environmental requirements. FCC is the electromagnetic compatibility threshold for the US market. These three constitute the "basic certification layer" for industrial control PCs circulating in major global markets. Lacking any one of them closes the corresponding market door. Their value lies not in proving how good the product is, but in proving that the product is not illegal or dangerous.
The next level of certification begins to touch upon the systemic nature of quality control. ISO 9001 quality management system certification covers the factory's production processes, quality inspection points, non-conforming product control, and continuous improvement mechanisms. It's not targeted at a specific model, but rather audits whether a company has the ability to consistently output qualified products. For buyers, the significance of ISO 9001 lies in answering a long-standing question in industrial product procurement: the sample you give me is good, but will subsequent batches be the same? The existence of a quality management system transforms this question from "trust" to "being monitored."
Further certifications delve into the deeper needs of specific scenarios. This is where the value of certificates truly differentiates. IP protection rating certification measures the degree of protection a device offers against intrusion of foreign objects and water. For industrial control all-in-one computers, IP65 means complete dustproof and low-pressure water spray protection—a crucial requirement for food processing workshops, outdoor self-service terminals, and pharmaceutical cleanrooms. However, the value of IP certification lies not in the certificate itself, but in "who conducted the testing, under what conditions, and whether every product consistently maintains the same rating"—some manufacturers' IP65 reports only address the submitted samples, not mass production consistency. Experienced buyers won't just look at the certificate; they will inquire about the testing conditions and batch consistency commitments.
EMC directive testing for electromagnetic compatibility (EMC) certification is a common compliance certificate in conventional industrial environments, but its importance rises dramatically in medical settings. If a medical industrial control computer shares the same electromagnetic environment with life support equipment, monitors, and infusion pumps, insufficient EMC performance could lead to malfunctions in other devices. Therefore, the EN 60601 series standards specifically for medical devices are far more stringent than general industrial EMC certifications. In this context, the value of the certificate is no longer passive compliance, but proactively ensuring patient safety—a classic example of how the value of a certificate is enhanced by the specific application scenario.
Explosion-proof certification takes the specificity of these scenarios to the extreme. Petrochemical plants, underground coal mines, and workshops with high dust explosion risks require industrial control computers to have ATEX or IECEx explosion-proof certification. Obtaining these certifications is extremely costly, involves long testing cycles, and results in a very limited number of certified companies. In such scenarios, the explosion-proof certificate almost directly determines the scope of the supplier shortlist; its value is not a "bonus" but rather the "only option."
While RoHS and REACH certifications may seem to have low barriers to entry, in trade exported to the EU, they represent the red lines of regulations regarding hazardous substance restrictions and chemical compliance. Non-compliance can lead not only to returns but also to customs rejection and market bans for the entire shipment. At this point, the value of the certificates shifts from a technical level to a risk management aspect related to trade compliance.
Even if the entire certification system were listed and analyzed step by step, it would only solve the problem of "how to select qualified suppliers," but not the deeper question of "how to choose a brand partner for long-term cooperation." This is because certificates examine the static indicators of a product at a specific point in time, while cooperation tests a company's response and decision-making priorities in a dynamic environment.
The true nature of an industrial control PC brand is often revealed in collaborations beyond certifications. When project delivery issues arise, does the brand's first reaction involve revisiting contract terms to define liability, or sending engineers to the site to restore production? This choice reflects the company's values, which no certification can measure. Three years later, if a customer wants to order an additional batch of the same model, can the brand continue supplying, maintain backward-compatible hardware versions, and provide six months' advance notice of the end-of-life (EOL) discontinuation plan for key components? This commitment to supply continuity is a more solid foundation for long-term cooperation than any certification. When a customer requests a non-standard customization option, outside the standard configuration, does the brand refuse, offer a higher price to discourage customers, or organize an engineering team to carefully assess feasibility and provide a solution? This willingness and ability to respond technically determines the upper limit of the partnership.
Going deeper, in extreme situations, a brand's decision-making logic comes to the forefront. When raw material prices rise across the board, will it unilaterally switch to lower-cost alternatives without consulting its customers? When core chips are in short supply, is it able to mobilize supply chain resources to prioritize deliveries to long-term customers? In these moments, all ISO processes and certifications may temporarily fall silent in the face of commercial interests. What truly matters is a company's years of accumulated credit record in the industry and its level of commitment to its brand reputation.
Therefore, experienced industrial product purchasers go through a progressively deeper process when evaluating suppliers: the first layer is checking whether the qualifications and certificates are complete—this is the bare minimum; the second layer is assessing the matching degree of the certificates to the corresponding scenarios—this is professional judgment; the third layer is looking at cooperation records and industry reputation beyond the certificates—this is long-term risk assessment. Only when all three layers are passed will the cooperation be upgraded from the transaction level to the partnership level.
 Implicit Collaboration Capabil
 Changes in device connection m
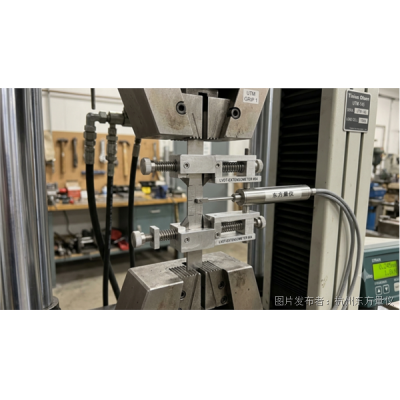 LVDT displacement sensor defor
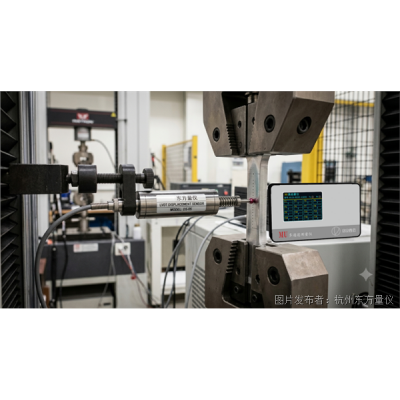 LVDT Displacement Sensor Mater